Infrastructure Automation and Terraform
Infrastructure automation with Terraform describes servers, networks, storage, certificates and firewall rules as files you can read, review and run again. An environment can then be recreated from those files, not from memory.
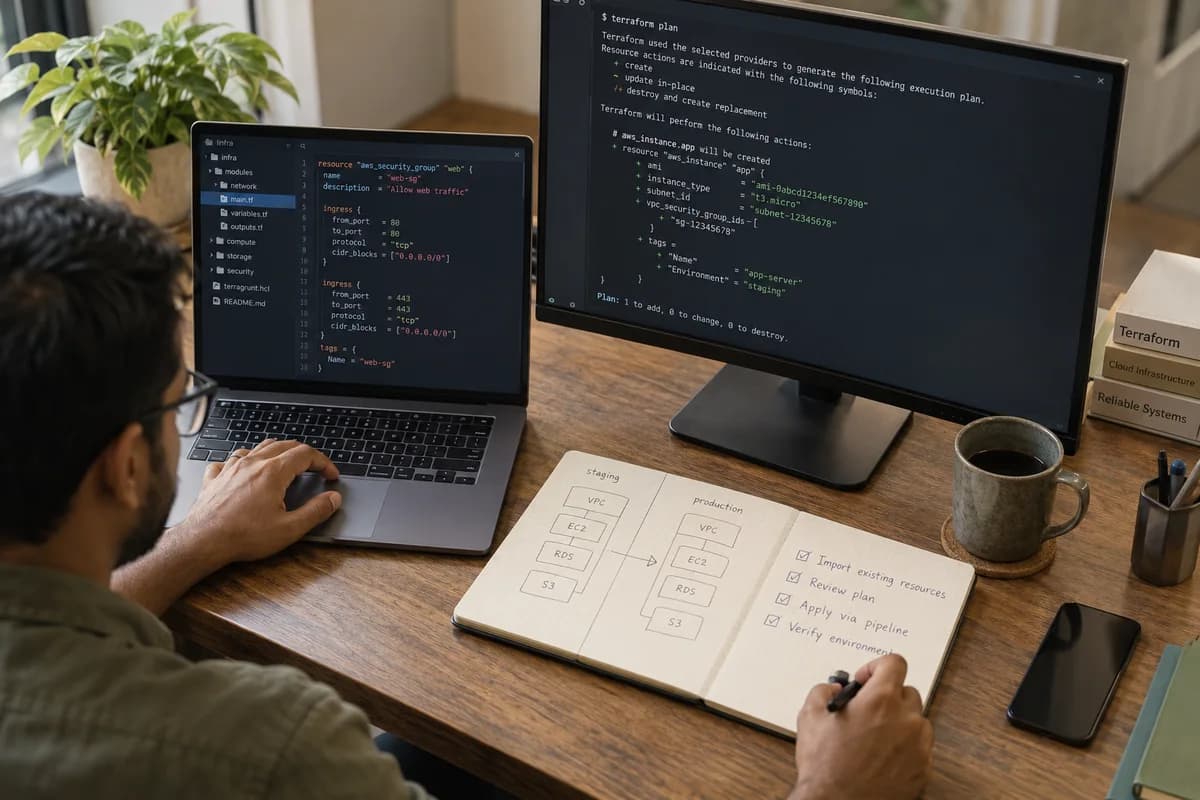
An environment nobody can rebuild
A firewall rule was added during an incident. A storage bucket was created for a one-off import and never removed. A certificate was uploaded by hand. None of it is written down, so a second environment never quite matches the first.
How the move is done
What stays outside the files
Passwords and keys do not belong in Terraform configuration. They are held in a secret store and referenced from it. Data is not managed this way either, because a tool that can destroy and recreate a resource should never point at your only copy of the database.
Frequently asked questions
Can infrastructure automation and Terraform be added to a live environment?
Yes, by importing the existing resources and not by rebuilding them. Nothing is recreated during that work, and the first plan should show no changes.
Does this lock us into one cloud provider?
The tool works with several providers, but the configuration you write is specific to the one you use. Moving clouds still means rewriting much of it.
Is it worth it for two servers?
Often not. Plain provisioning scripts are easier to live with at that size, and we would say so instead of adding complexity.
Who can apply changes?
Whoever you authorise, usually through the pipeline and not from a laptop. That keeps a record of every change to the environment.
Tell us what you need.
Share your requirements and one of our engineers will come back to you within one business day.
- No obligation
- A reply within one business day
- Your details stay private
Start with your requirements
Seven short steps that tell us what you need. An engineer reads them before getting in touch.
Share your requirements