In this guide 7 sections
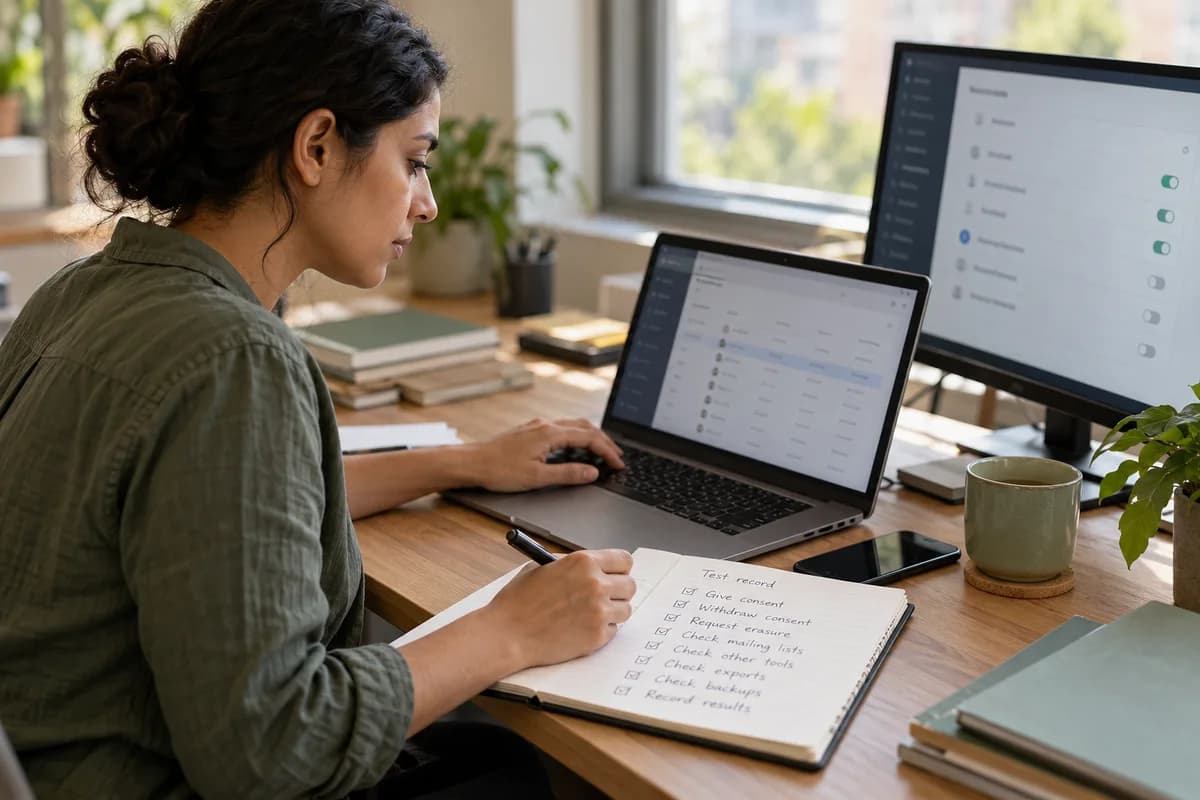
Test deletion and consent withdrawal with a test record that you follow end to end. Give consent, withdraw it, request erasure, then check every list, export and connected tool for copies. GullySystem’s data protection service verifies these paths, including what remains in backups, because they are often found not working.
Why these controls fail quietly
An opt-out often sets a flag in one system. The marketing tool connected last year never hears about it. Messages keep going out.
Deletion has the same weakness. The record leaves the main screen but survives in an export, a reporting copy or a shared sheet. Nobody notices until someone complains.
Run a test withdrawal end to end
Create a test person with a phone number and email address you control. Give consent through the normal form. Confirm the record shows purpose, date and source.
Then withdraw consent the way a customer would. Rule 3 of the Rules, as published, says withdrawal should be comparably easy to giving consent. Your lawyer can say how that applies to you.
- Withdrawal recorded with date and source
- Removed from live sending lists
- Removed from every connected messaging tool
- No further messages after a set wait
Test an erasure request the same way
Send an erasure request for the test person through the channel your notice names. Check who received it, how identity was confirmed and what was deleted.
Some records may need to stay. The Rules as published require certain processing logs to be kept for at least one year. Tax and sector laws may require invoices to be kept. Your lawyer sets those periods.
Record the outcome in plain words. Note what was erased, what was kept and why.
Check retention jobs and backups
A retention job that never runs looks the same as one that works. Look for its report. It should list what was removed and when.
Backups are harder. Removing one person from an encrypted backup is rarely practical. A common approach is to let old copies expire on a set schedule and keep a list of erasure requests to re-apply after any restore.
- Retention job report reviewed each cycle
- Backup expiry schedule written down
- Erasure list kept for re-applying after a restore
Record what you found and retest
Write each failure down with an owner and a fix date. Then repeat the same test after the fix.
The PIB backgrounder says requests for access, correction or erasure must be addressed within ninety days. Testing well before a real request arrives leaves time to fix what breaks.
Withdrawal and erasure test script
A step list for one test record: give consent, withdraw, request erasure, then check each system and tool. Each step has an expected result, an actual result and a pass mark. Keep the filled copy as evidence for the next review.
Open a blank worksheet to printQuestions owners ask
Can we delete one customer from our backups?
Usually not in practice. The common approach is a backup lifecycle so old copies expire, plus a record of erasure requests that is re-applied if a backup is ever restored.
Is an unsubscribe link enough for withdrawal?
Not on its own. The link must stop messages from every tool that holds the contact, not just the one that sent the email. Test each one.
How often should these tests run?
After any new tool, form or integration goes live, and at each scheduled review. A connected tool added for one campaign is a common cause of failure.
Sources
- Press Information Bureau backgrounder: DPDP Rules, 2025 Notified (17 November 2025) — verified 6 Oct 2026
- Digital Personal Data Protection Rules, 2025, Gazette of India notification G.S.R. 846(E) — verified 6 Oct 2026