Business solutions for Cybersecurity companies
Explore software for work such as “VAPT for web, mobile and API applications”. Review each business function below, including when it fits and what to check before implementation.
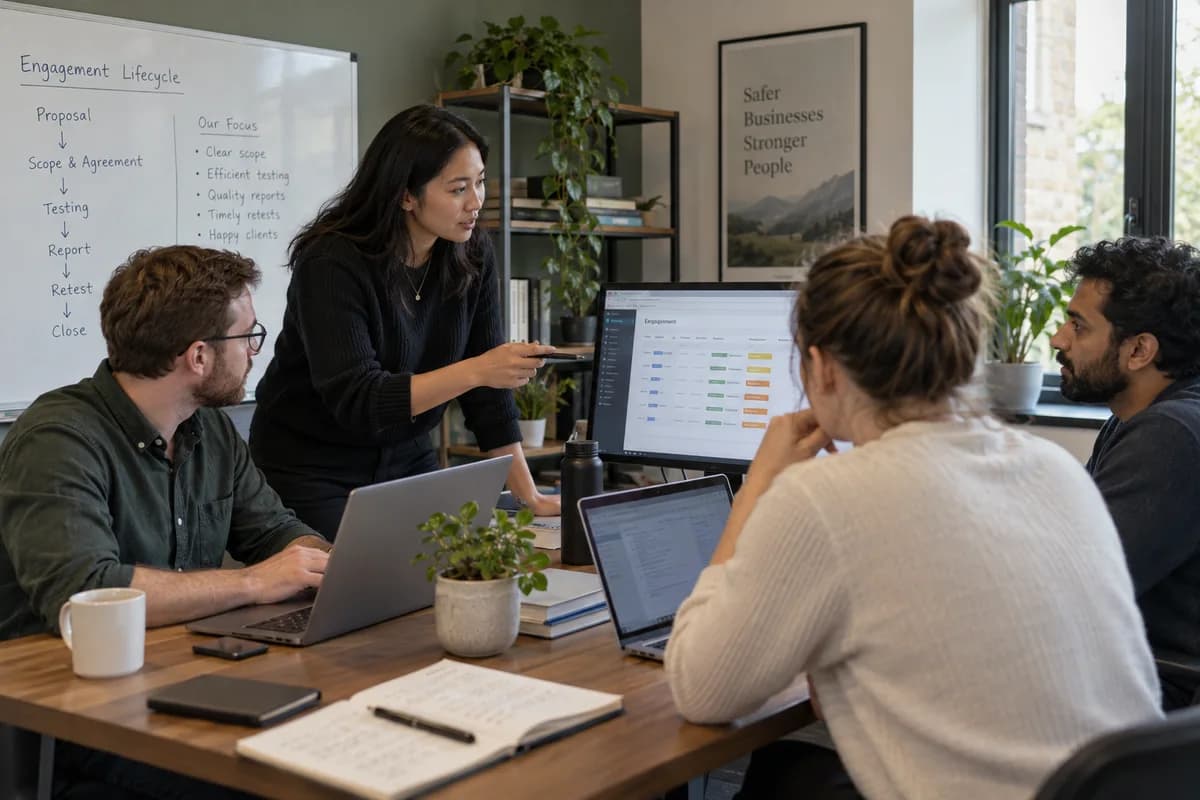
How the business operates.
Security work is sold as a scope: a set of applications, networks or cloud accounts, tested by named people for a fixed period. The record that matters is what was in scope, what was found and what has been fixed.
The records that hold the operation together.
- Prospects and scoping. Record each enquiry with the kind of test asked for, the targets, the constraints and the questionnaire answers. Build the proposal from the firm’s own day rates and keep every revision.
- Engagement register. Hold each engagement with client, test type, window, assigned testers and stage, from proposal through report issue and retest, so the whole bench can be read in one list.
- Scope and rules of engagement. Store the signed scope, the in-scope and excluded hosts, the allowed hours and the client’s emergency contact. A tester opens the rules before touching a single target.
- Tester allocation. Show which testers are free, which certifications and specialities each holds, and which weeks are already booked, before a start date is promised to a client.
- Findings tracker. Log each weakness once, with affected asset, severity, evidence, steps to reproduce and fix advice. Follow it from open to fixed to retested and closed.
- Report drafting and review. Pull approved findings into the report template, record who reviewed and signed off, and keep every issued version. The finished file leaves as a protected download.
- Retests and fix checks. List the findings a client says are fixed, schedule the retest, and record the result per finding. The retest letter is produced from those results.
- Retainers and monitoring hours. Set monthly hours per client, log alert handling, advisory calls and tuning work against the plan, and show used and remaining hours before the invoice is raised.
Operational bottlenecks to check
Scope lives in an email thread
Which hosts were in scope, and which were excluded, is argued after the report is sent. The thread has the answer somewhere.
Findings sit in tester notes
Each tester keeps findings in a personal file and the report is stitched together at the end. Duplicates and gaps get through.
Retests are forgotten
The client fixes issues and nobody tells the firm. A retest is offered months later, or not at all.
Retainer hours are not counted
A monitoring client uses far more hours than the contract covers, and no report shows it. The pricing stays the same.
Licence renewals lapse
A resold firewall subscription runs out on a Friday. The client’s protection ends before anyone has quoted the renewal.
Follow the work across teams.
This is a planning flow. Confirm the steps, owners and approval rules against your actual operation.
Roles and responsibility boundaries.
Reports your managers need.
- Engagements by stage, test type and assigned tester
- Findings by severity, affected asset and status
- Reports awaiting review, with the reviewer and days waiting
- Retests requested, done and still open, by client
- Retainer hours used and remaining, by client and month
- Licences and subscriptions due for renewal, with quote status
- Tester bench use against booked and free days
Connections to scope
- Calendar
- Ticketing or monitoring alert feed
- Document signing
- Accounting export
- Messaging for client updates
Confirm data access, record ownership and the exchange method for each connection. Inclusion here does not mean every connection is available in a standard package.
Setup decisions and adoption risks.
Use these requirements to plan phases, data migration and user training. Agree the release sequence after reviewing your current systems.
Limitations to settle before implementation
- A solo consultant with two or three clients a year can run on a proposal template and a folder of reports.
- Product companies that build and sell their own security software will find SaaS Company Management Software closer.
Modules to consider first.
These functions connect to the operating model above. Confirm each one against the work your business actually runs.
Choose the operation you want to improve.
Use these activities to explain your scope. Your business does not need every function in the directory.
- VAPT for web, mobile and API applications
- Annual assessment renewals
- SOC monitoring and managed detection retainers
- ISO 27001 implementation and surveillance audit support
- SOC 2 readiness for SaaS companies selling abroad
- Regulator-driven assessments for banks, NBFCs, brokers and insurers
- Personal data protection readiness under India's data protection law
- Red team engagements for large enterprises
- Security awareness training and phishing simulations
Explore the business functions.
Production, stock, fleet and recurring billing functions apply only where your business runs those activities. Read the suitability conditions on each page.
Platform
Audit Trail
Record who changed important business data and when.
View workflow and suitability →Roles and Permissions
Control which records and actions each user can access.
View workflow and suitability →Workflow and Approvals
Route business requests through defined approval steps.
View workflow and suitability →
Documents
Project Management
Project Management Reports
Compare project progress, effort and costs with the agreed plan.
View workflow and suitability →Project Time Tracking
Record time against projects and tasks with billable status.
View workflow and suitability →Resource Allocation
Allocate people and shared equipment to project work.
View workflow and suitability →
CRM
Field Service
Helpdesk
Start with the problem your team can describe.
Bring a sample record and show where information is copied, missed or waiting for approval. Scope the first useful change from there.
What happens after you share your requirements
- We review your brief and the systems you already use.
- We clarify the workflow, missing information and the work to consider first.
- The proposed scope sets out the deliverables, responsibilities and dependencies.
- Review the scope and commercial terms before deciding whether to proceed.
Start with your requirements
Describe your current process, the people involved and the change you need. Start with the details you know; we can clarify the rest together.
Share your requirements