ISO 27001, SOC 2 and Privacy Law Readiness
This service covers the technical half of preparing for ISO 27001, SOC 2 and privacy law compliance. It includes access reviews, logging, encryption, backups and filed evidence. Certification itself is decided by an auditor.
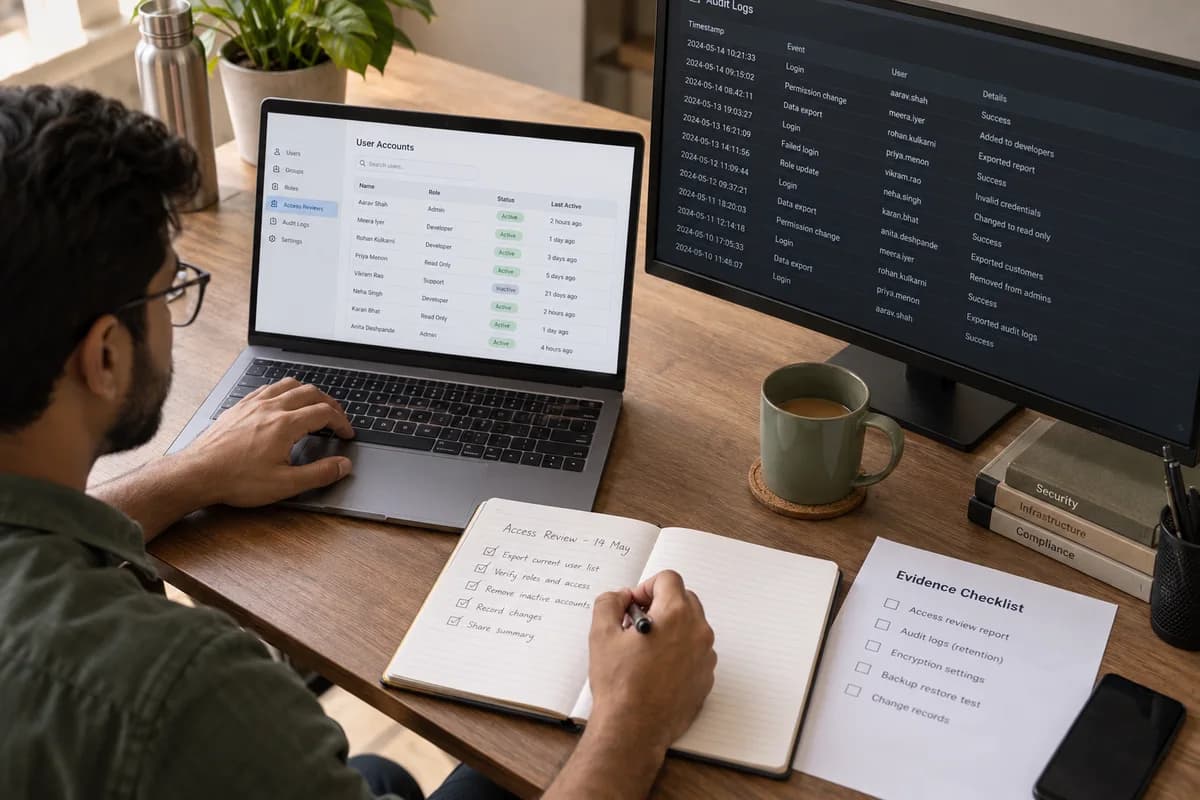
Technical controls auditors ask about
What sits outside our work
- We do not issue certificates and are not your auditor or certification body
- Policy wording, contracts and legal position belong with your consultant or lawyer
- A standard is not a product. Most of the effort is your team changing habits
- No pass can be promised for any audit
Where privacy law sits apart
ISO 27001 and SOC 2 are standards you choose to pursue. Privacy laws such as the GDPR concern personal data, and whether and how they apply is a question for your legal adviser. Your adviser reviews the configuration before launch, and again when a local rule changes. Much of the technical work overlaps. Three items are particular to privacy law: recording why data was collected, acting on a deletion request, and knowing which vendor holds a copy.
Frequently asked questions
Can GullySystem certify us to ISO 27001?
No. A certificate comes from an accredited body after its own audit, and the auditor must be independent of whoever did the work. We do the engineering that audit will examine, plus the evidence pack.
Does privacy law apply to our business?
That is a question for your legal adviser. What we can show is which personal data your systems hold, where it flows and who else keeps a copy. That is the fact base your adviser needs.
Our customer sent a security questionnaire. Do we need full certification to answer it?
Usually not. Many questionnaires can be answered with evidence: a recent test report, an access review, a restore record and a written policy. Certification becomes useful when several large buyers send the same questionnaire each year.
Tell us what you need.
Share your requirements and one of our engineers will come back to you within one business day.
- No obligation
- A reply within one business day
- Your details stay private
Start with your requirements
Seven short steps that tell us what you need. An engineer reads them before getting in touch.
Share your requirements