Penetration Testing Through Qualified Specialists
Penetration testing is a controlled attempt to get in, inside a boundary you approve in writing. Specialists work through your application, API or network, and you keep the steps, evidence and retest result.
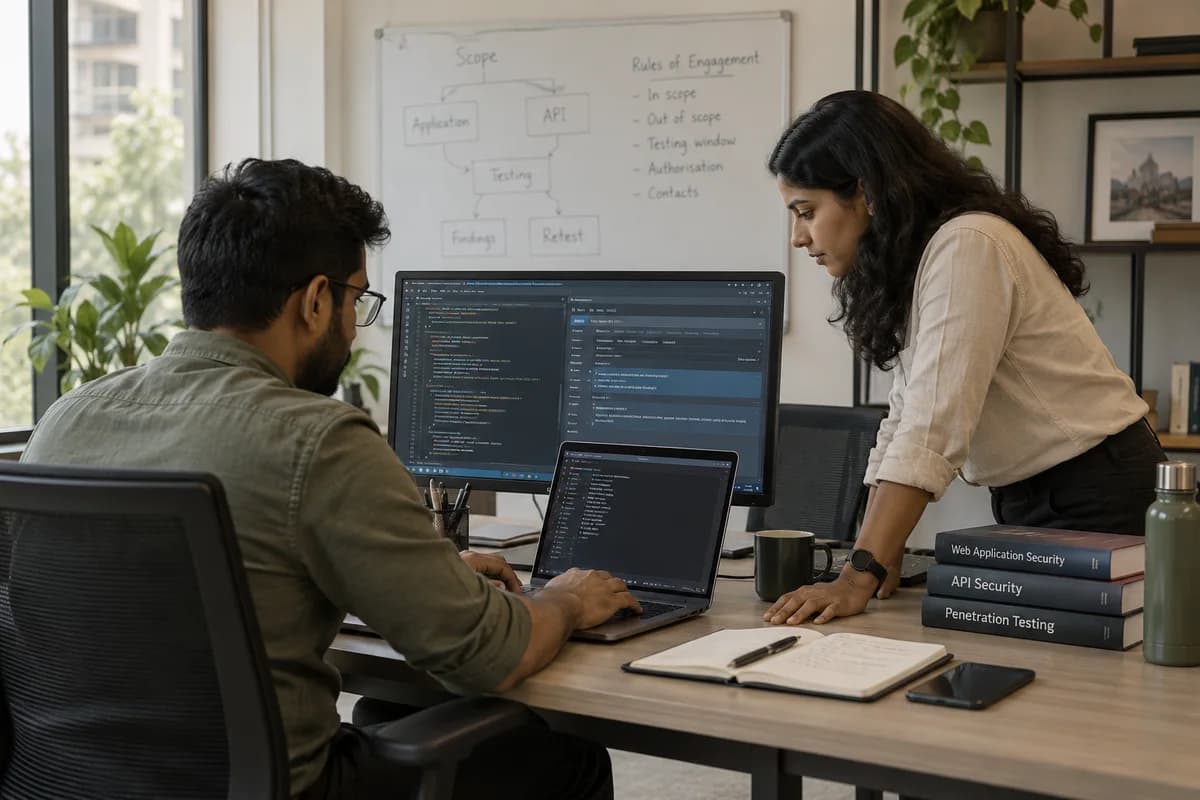
Rules of engagement come first
Nothing starts until the boundary is written down and signed. The document states what is in scope, what is out, which hours testing may run, who authorises each system, and who can be reached by phone if something goes wrong. Your hosting provider may need to be told as well.
What a test produces
Notes before you commission one
- A test is a snapshot of one week, and a large release changes the picture
- A brochure website with no login and no customer records rarely needs one
- Multi-factor, account cleanup and a tested backup reduce risk at low cost
- Ask who will be on your test and what they have tested before
Frequently asked questions
Who actually carries out the penetration testing?
Specialists engaged for that scope, named to you before work begins. You are told what kinds of systems they have tested before and who your contact is during the window.
Should the test run on our live system or a copy?
A recent copy is safer where one exists, because nothing done there can disturb a real record. Some findings only appear in the live setup. Those are tested live, under tighter limits and inside agreed hours.
How is this different from a vulnerability assessment?
An assessment lists what looks wrong across a wide surface. Testing tries to exploit a handful of those items for real. Running the assessment first usually shows where testing is worth pointing.
Can we share the report with a customer who asked for it?
Yes. The report is yours. A summary without the reproduction steps is usually safer to hand over, and we prepare that version on request.
Tell us what you need.
Share your requirements and one of our engineers will come back to you within one business day.
- No obligation
- A reply within one business day
- Your details stay private
Start with your requirements
Seven short steps that tell us what you need. An engineer reads them before getting in touch.
Share your requirements