Secure Code Review
Secure code review is a person reading the parts of your codebase where some problems never show from outside. Examples are session handling, permission checks, payment logic and database queries.
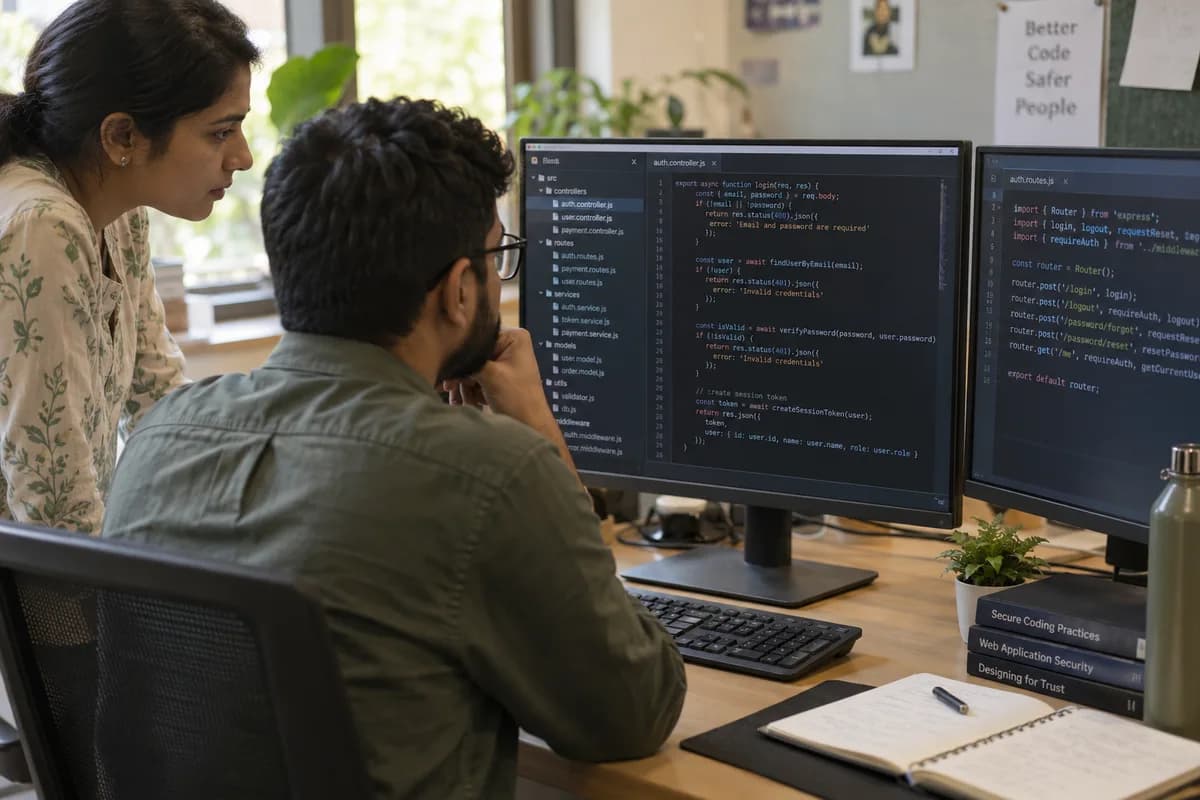
The files opened first
How findings reach your developer
Each finding names the file, the line and the condition that triggers it, so nobody has to hunt for it.
- The file and line, with the surrounding code quoted
- The input or sequence that makes it fail
- The shape of a fix, not a lecture on general principles
- A severity, plus one sentence on the impact if it is used
When a review is the wrong spend
- The application is mid-rewrite, so many findings would be deleted anyway
- The basics are not done yet: shared admin logins, ex-staff accounts, no multi-factor
- The code belongs to a vendor who will not grant repository access
- You need proof of what an outsider can reach, which source review cannot give
Frequently asked questions
Do you need full access to our source code?
Read access to the repository is enough, and it can be limited to the parts in scope. If your team prefers, we review a copy you provide. What we hold, and for how long, goes into the engagement note.
Can you review code written by a vendor who has left?
Yes. Inherited code takes longer because little is documented and earlier decisions must be worked out from the code itself, one file at a time. We say upfront which parts are unreadable enough to be worth rewriting.
Does a secure code review replace testing the running application?
No. Reading code finds what is written wrong. Testing the live system finds what is configured or deployed wrong. A business holding customer records usually needs both, often the running application first.
Tell us what you need.
Share your requirements and one of our engineers will come back to you within one business day.
- No obligation
- A reply within one business day
- Your details stay private
Start with your requirements
Seven short steps that tell us what you need. An engineer reads them before getting in touch.
Share your requirements