PCI-DSS Compliance for E-Commerce
PCI-DSS is the card industry’s standard for handling card data, and the simplest way to reduce its scope is to never hold that data. Checkout sends cards straight to your gateway.
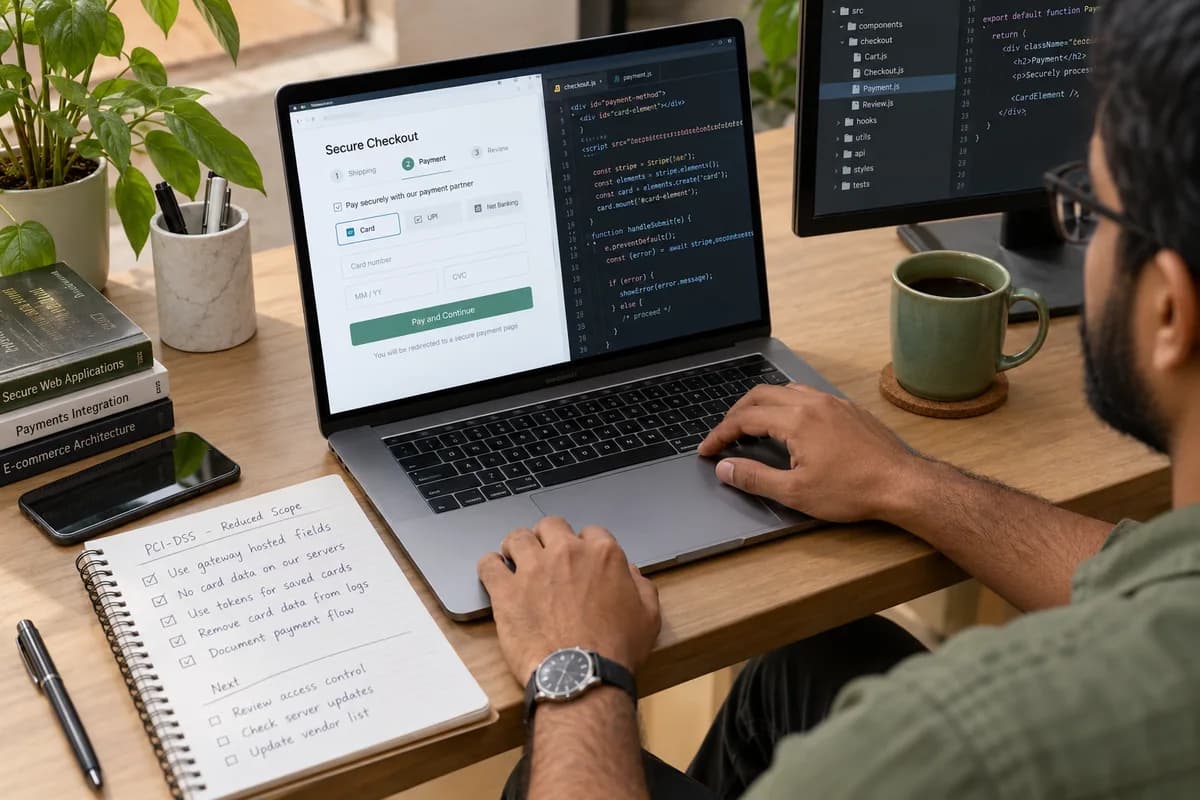
Keeping card data off your servers
Every card number stored on your server widens what has to be protected and audited. Most online stores have no need to hold one.
What remains with the merchant
Reduced scope is not zero scope. Some obligations stay with the merchant whatever the checkout looks like.
What we do and do not claim
Owners are sometimes sold certainty that nobody can supply. Our claims are limited to what we build.
Frequently asked questions
Does PCI-DSS apply to a small Indian store?
Yes, in proportion. A merchant accepting cards has obligations. A store on hosted checkout that stores no card number usually has the shortest questionnaire, and your acquirer confirms what applies.
Can we save customer cards for faster checkout?
Yes, through your gateway’s tokenisation. That is the only route we implement. Storing card numbers yourself brings audit obligations that a small store should avoid.
Will you certify our store?
No. Certification is issued by a qualified assessor or your acquiring bank. The store is built, configured and documented so that an assessment is straightforward.
Tell us what you need.
Share your requirements and one of our engineers will come back to you within one business day.
- No obligation
- A reply within one business day
- Your details stay private
Start with your requirements
Seven short steps that tell us what you need. An engineer reads them before getting in touch.
Share your requirements