Cloud Security Management at the Infrastructure Layer
Cloud security management reduces what your infrastructure exposes and controls who can reach it. It covers network rules, named accounts, secret storage and a patch schedule that somebody keeps.
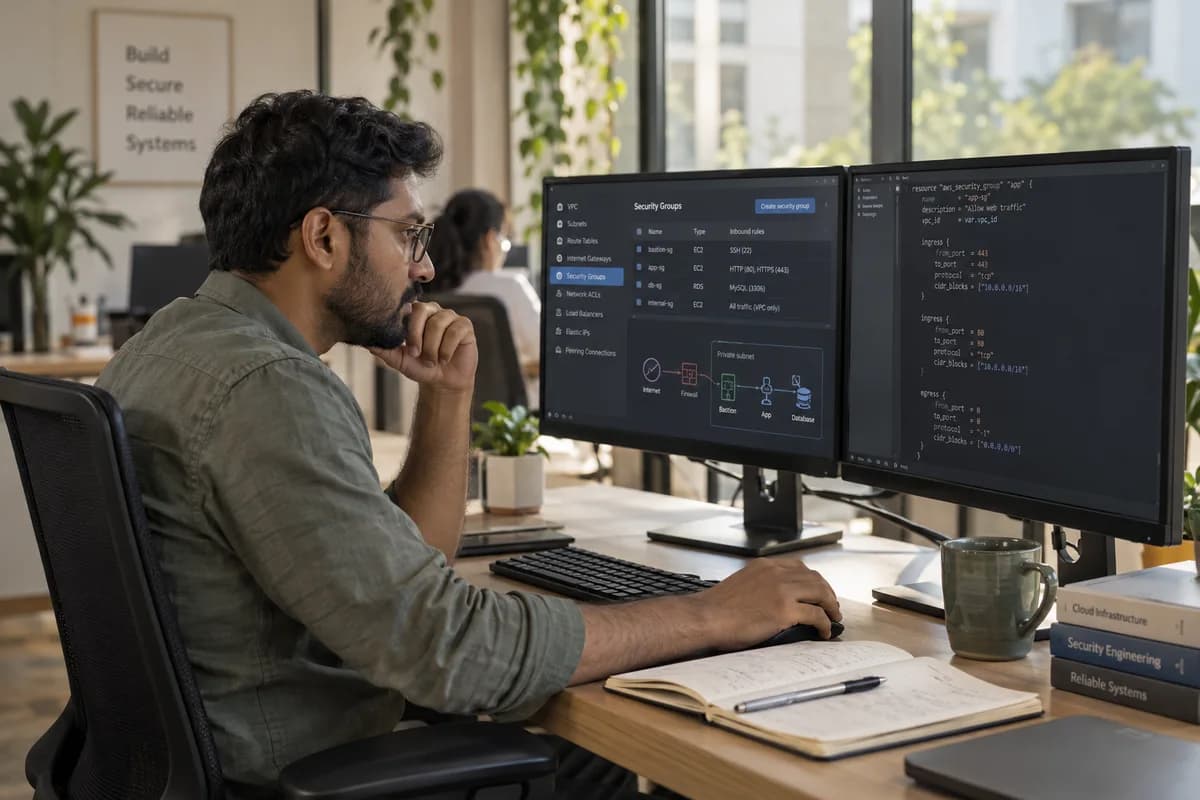
What a review usually finds first
- Administrative ports reachable from the open internet
- One shared console login used by everyone who needs any access
- Database passwords stored in the code repository where any developer can read them
- Patches left unapplied because no window was agreed to test them
Closing the exposed points
Where the boundary sits
This work covers the infrastructure layer: what is exposed, who can reach it, and how access is controlled and logged. Flaws inside your own application code are a separate discipline, and so is formal penetration testing. Where that is the gap, you are told.
Frequently asked questions
How is cloud security management different from monitoring?
Monitoring reports that something is wrong. Security management reduces what can go wrong, through fewer open ports, fewer shared credentials and fewer machines running old patches.
Does this include testing our application code?
No. Application security review and penetration testing are separate work with different skills. Where that is what you need, we say so.
Will tightening access disrupt how our team works?
Somewhat, and by design. Shared logins are replaced with named ones, and people notice the change. Rollout is agreed with you beforehand.
Who holds the keys and credentials afterwards?
Your business does, in your own secret store. Our access is named, scoped and can be removed whenever you decide.
Tell us what you need.
Share your requirements and one of our engineers will come back to you within one business day.
- No obligation
- A reply within one business day
- Your details stay private
Start with your requirements
Seven short steps that tell us what you need. An engineer reads them before getting in touch.
Share your requirements